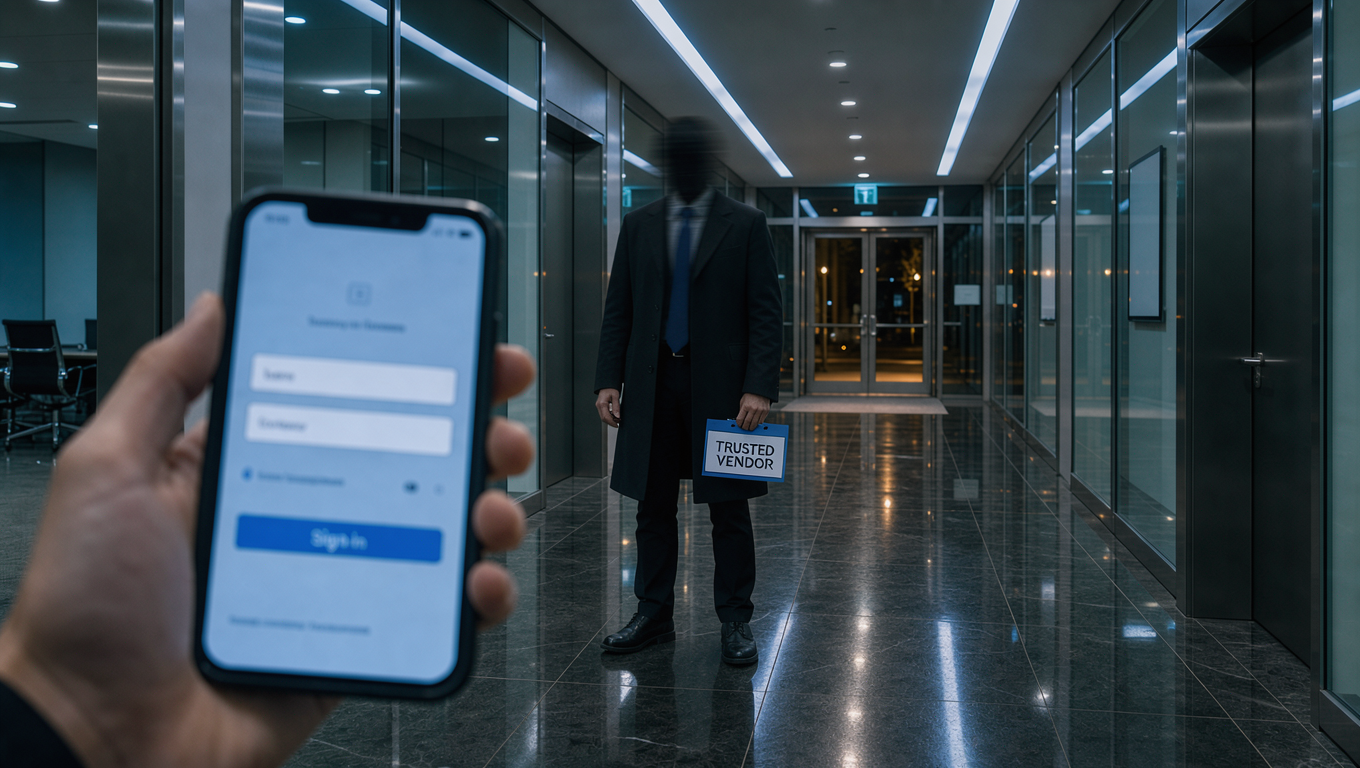
Featured image & Video: AI-generated in collaboration with Mistral Vibe, using the FLUX model by Black Forest Labs. No stock photo, no photo of a real person or real company. The scene is a staged visualization of the attack pattern described in this post. Both tools are based in Europe and are therefore compliant with the EU AI Act.
A few weeks ago, I built a small demo. “SpaceRanger Club.” A fake login page. It looks harmless, like any members-only sign-in.
Here is the trick: the moment you click “Log in”, your input is sent to a server that has nothing to do with this page. No download, no warning, no second interaction. The evil is already inside the code itself, like a note inside a letter.
I built it to prove one point: malicious software does not need a vulnerable user. It is enough for the login process itself to become the weapon.
On November 16, that is exactly what happened. Not as a demo.
Attackers abused the account registration process of a third-party vendor (Optimizely, a web personalization platform) to inject malicious JavaScript into customer projects. The result: 178 corporate websites, including GitLab, IKEA, Salesforce and Zoom, loaded malware into visitors’ browsers on simple page view. A card skimmer, cookie and screenshot theft, a crypto clipper that swaps copied wallet addresses in your clipboard. More than $7,000 had already been stolen before anyone noticed.
The real lesson:
The attack did not come through the door. It was already standing in the hallway, because someone had issued it a visitor’s pass.
None of the 178 customers did anything wrong. Every single one of them had allowed a third party to run code on their page, and that is exactly where the attack surface lived. Not at their own server. Not at the user. In between.
So here is my question to everyone running a website, however small it may be:
Do you know which third-party scripts run on your login page, and who administers those accounts?
If the answer is “no”, then your security perimeter is not your server. It is the last vendor in your loading chain.
My demo is here (harmless, of course, nothing is actually sent): https://futureorg.digital/andy-s-login-demo-the-invisible-trap.html